Analysis and assessment
Audit
Stick.
Portable software for an agentless, non-destructive assessment of your IT environment – with clear context instead of a flood of raw data.
Clarity about your IT
Know what exists and what can be reached.
IT environments grow. Systems are added, services remain and responsibilities change. AuditStick creates a reliable overview.
It examines systems and networks without agents and without making changes. Operating systems, reachable services, network segments and other infrastructure characteristics are collected and assessed in a structured way.
Not every open port is automatically a security incident. What matters is the context: What exists? What is reachable? What is configured correctly? Where is evidence missing? And where is a closer examination required?
- No installation on target systems
- Explicitly defined and authorised audit scope
- Security score, traffic-light assessment and separately identified coverage gaps
- PDF and HTML reports with practical recommendations
Product view
From project setup to the final result.
Three views document the process from the first step to the final result.
The auditor first creates the project, then defines the authorised scope and selects the required modules. After the run, findings, coverage gaps and priorities are brought together in a clear result.
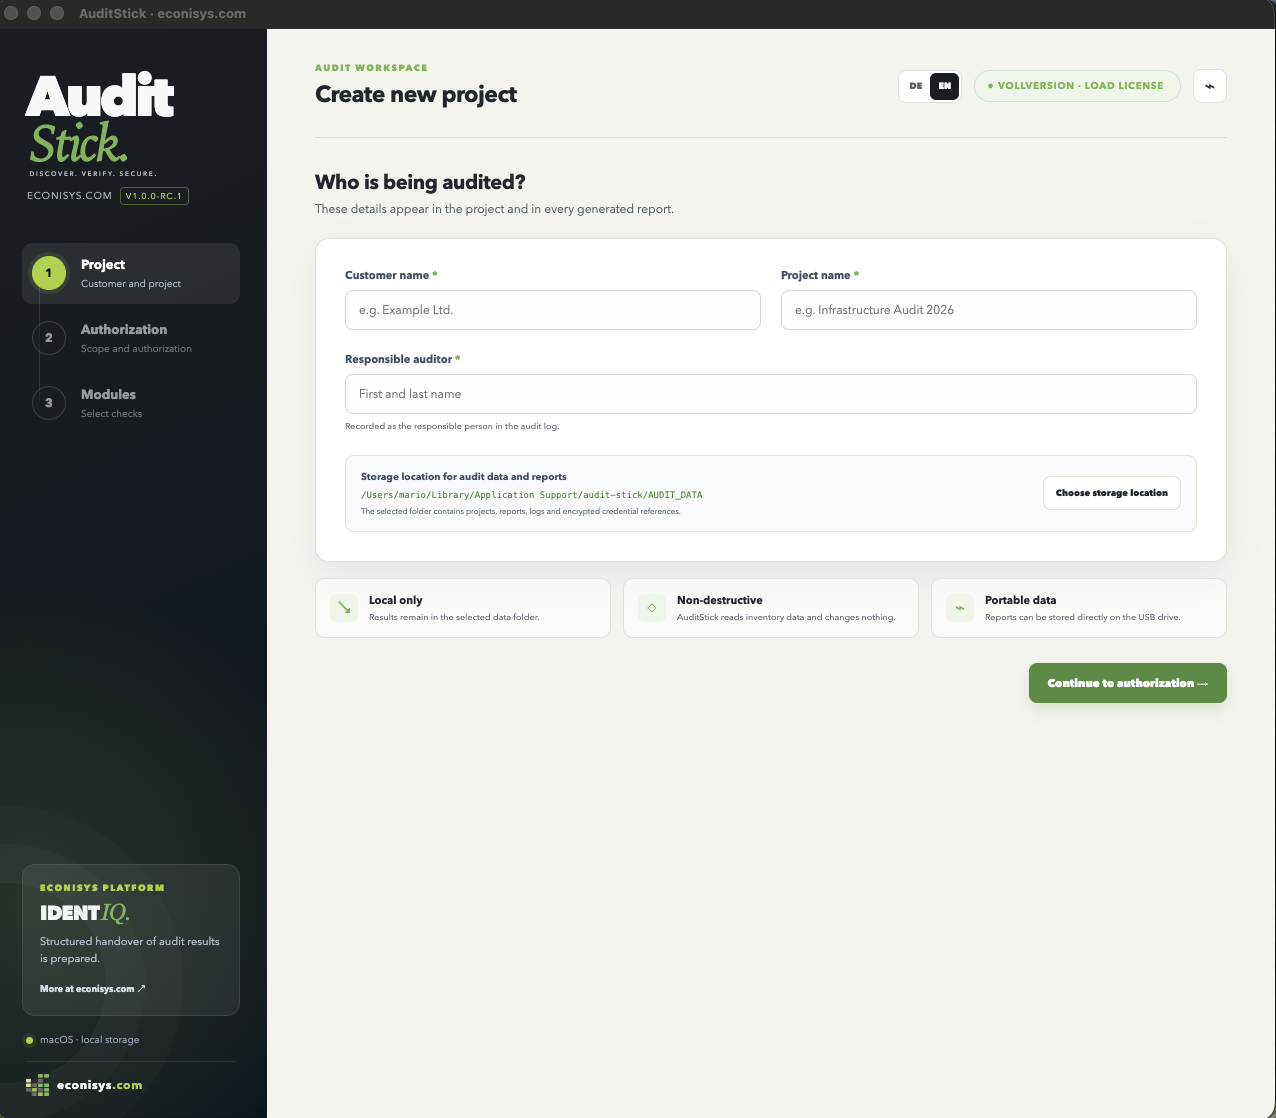 Project and audit details
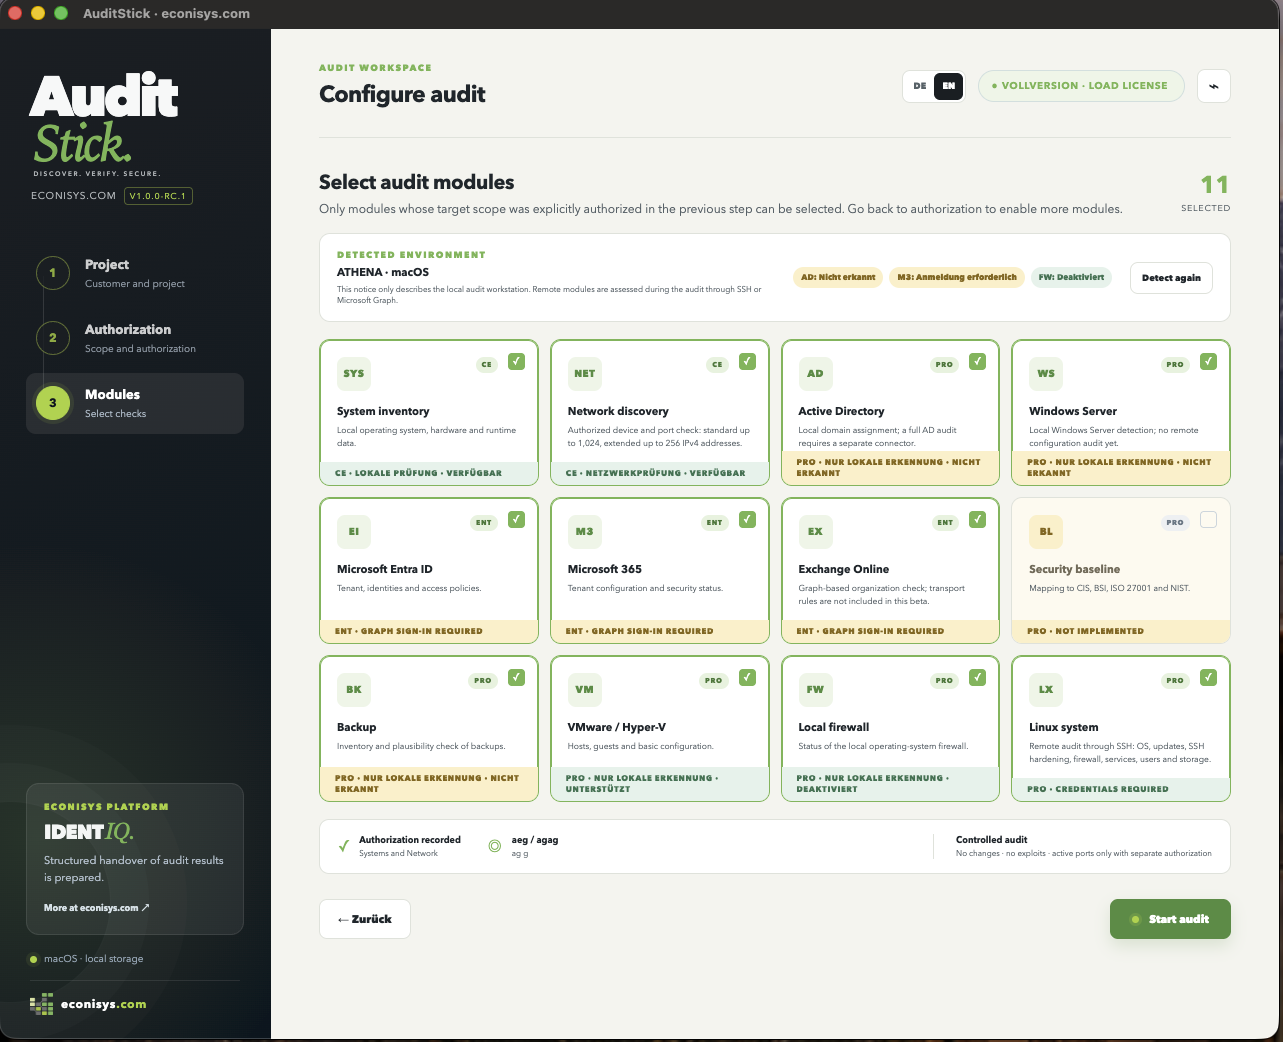 Audit scope and module selection
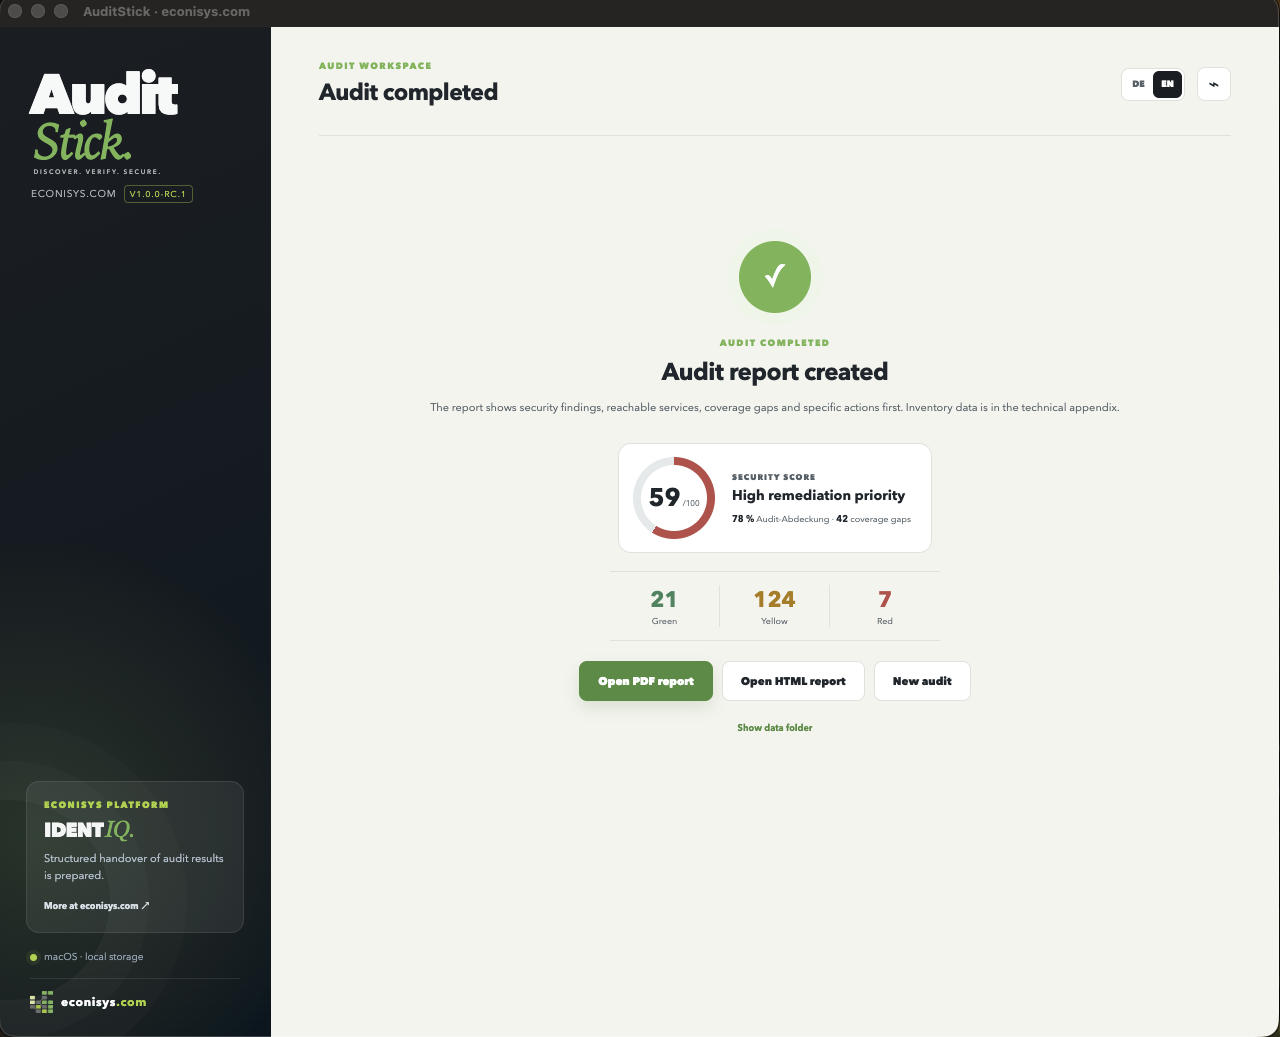 Security score and result overview
Process
Define the scope. Analyse. Decide.
Systems, networks and modules are explicitly authorised before the audit begins.
AuditStick reads inventory and status data without modifying the target systems.
Findings, passed controls and coverage gaps are reported separately.
The essential difference
Decision support instead of data overload.
Which edition fits?
CE is a practical entry point for one local network. PRO adds corporate networks, Windows, Active Directory, virtualisation and backup. Enterprise adds cloud and Microsoft 365 assessments.